Introduction
Cybersecurity has always been a race. Defenders build walls; attackers look for gaps. That race has accelerated dramatically as artificial intelligence enters the picture on both sides. Organizations are dealing with more devices, more data, more cloud services, and more sophisticated attacks than ever before — and traditional security approaches alone are struggling to keep pace.
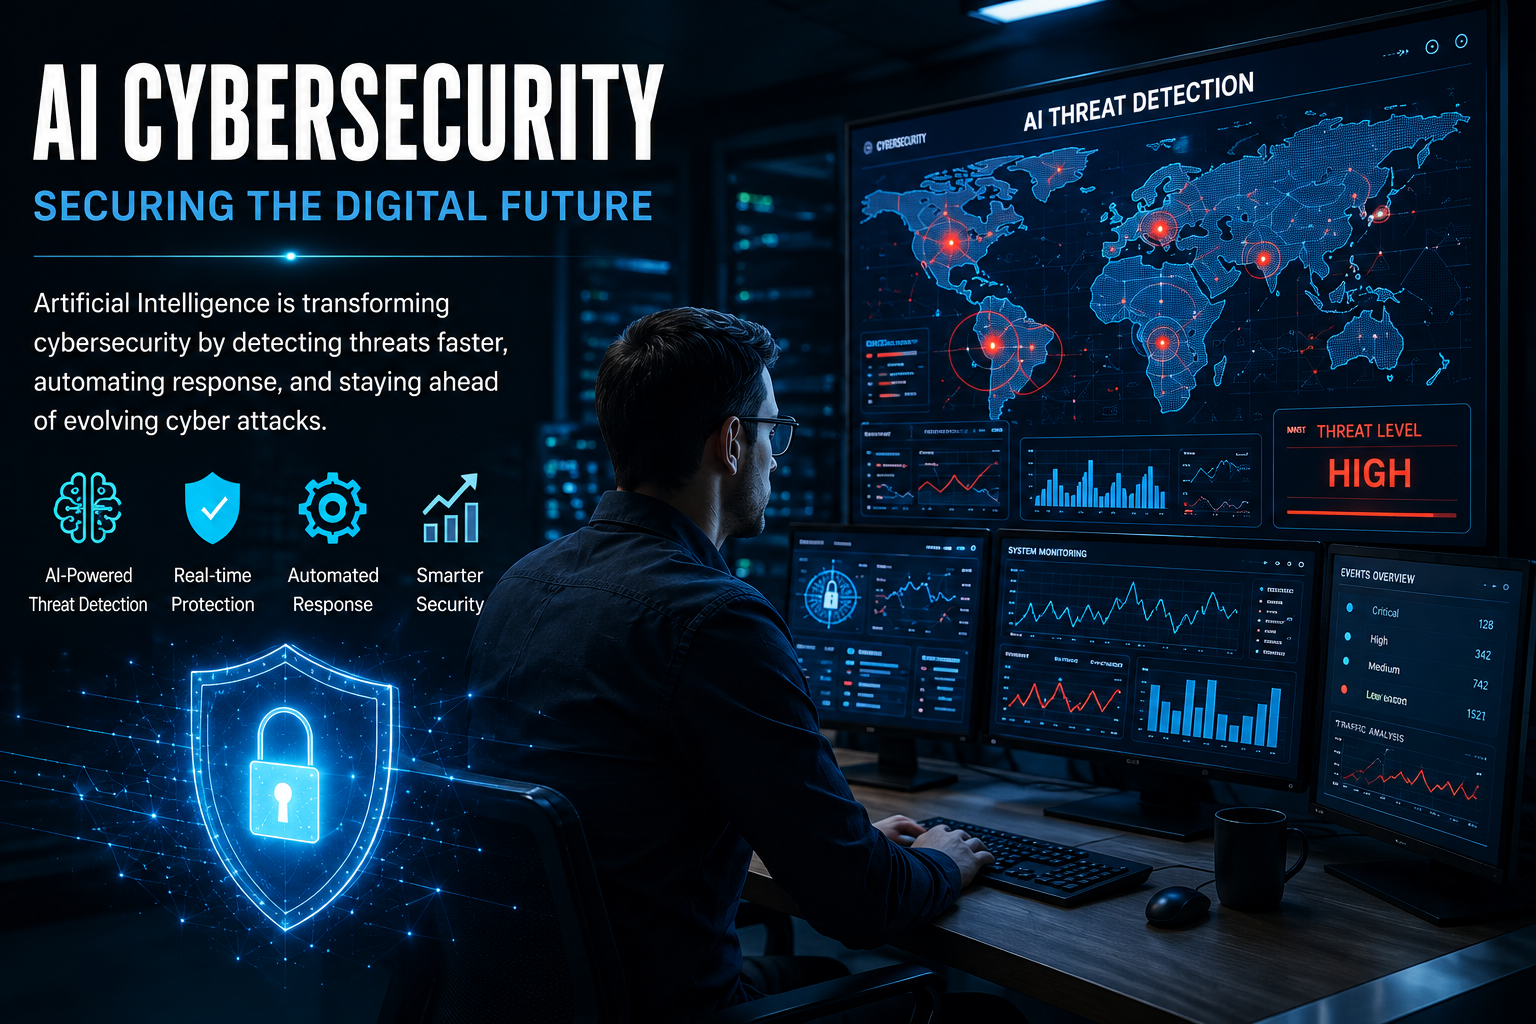
Artificial intelligence in cybersecurity is changing how security teams detect threats, respond to incidents, and protect networks at scale. AI can process enormous volumes of security data far faster than any human team, spot patterns that would otherwise go unnoticed, and help analysts prioritize what actually matters in a sea of alerts.
But AI is not a one-sided advantage. Attackers are using the same technology to generate more convincing phishing emails, create realistic deepfakes for impersonation, and automate parts of their operations. Meanwhile, AI systems themselves introduce new security risks that organizations need to understand and address.
This guide covers what AI cybersecurity means, how AI works in security environments, where it is applied, what benefits and limitations it brings, how hackers are using it, what threats target AI systems directly, and what all of this means for the future of cybersecurity and the professionals who work in it.
What Is AI Cybersecurity?
AI cybersecurity refers to the use of artificial intelligence and machine-learning techniques to identify, analyze, prevent, prioritize, and respond to cybersecurity threats.
In plain terms, it means applying AI to the problem of keeping computer systems, networks, data, and people safe from attackers. Rather than relying entirely on manually written security rules or known attack signatures, AI-powered systems learn from data, recognize patterns, and can flag behavior that looks suspicious — even if that specific attack has never been seen before.
AI cybersecurity is not a single product or technology. It is a broad approach that spans threat detection, malware analysis, network monitoring, identity security, security operations, and more. Organizations may use machine learning models, deep learning, natural language processing, and increasingly generative AI across different parts of their security stack.
How AI Cybersecurity Differs From Traditional Cybersecurity
Traditional cybersecurity has relied heavily on known threat signatures, manually defined rules, and human analysis. That approach works well for known threats but has limitations when attackers change tactics, operate at high speed, or disguise their activity as normal behavior.
| Traditional Cybersecurity | AI Cybersecurity |
|---|---|
| Rule-based detection | Behavioral detection |
| Known threats | Known + emerging patterns |
| More manual analysis | Greater automation |
| Signature-based detection | Anomaly-based detection |
| Human-led response | AI-assisted response |
It is important not to overstate the contrast. AI does not replace traditional security — it extends it. Modern organizations typically benefit from combining layered security approaches, including both established controls and AI-powered capabilities.
How Does AI Work in Cybersecurity?
Understanding how AI functions in a security context makes it easier to evaluate what it can and cannot do. The general process involves several connected stages.

1. Data Collection
AI security systems draw on large volumes of data from across the environment. That can include network traffic logs, authentication activity, endpoint behavior, system event logs, application activity, and email signals. The quality and breadth of this data matters: an AI system is only as good as what it can observe.
2. Pattern Recognition
Once data is collected, machine learning models look for patterns. During a training phase, models learn what normal activity looks like — typical login times, usual data transfer volumes, standard application behavior — so they can later recognize when something deviates from that baseline.
3. Anomaly Detection
Anomaly detection is one of AI’s most practical contributions to cybersecurity. Consider this example: an employee typically logs in on weekday mornings from a single city, accesses a modest set of business applications, and transfers normal-sized files. Suddenly, a login appears from a different country in the middle of the night, followed immediately by access to sensitive financial records.
That combination of signals — unusual location, unusual time, unusual resource access — is the kind of pattern AI can flag quickly. It is worth noting that an anomaly is a signal worth investigating, not automatic proof of an attack. Legitimate travel or unusual work circumstances can produce similar signals. Human review remains important.
4. Threat Classification
Beyond flagging anomalies, AI models can help classify what kind of suspicious activity may be occurring — distinguishing, for example, between a potential credential-stuffing attempt and ransomware staging behavior. Classification helps analysts understand the nature of a threat more quickly.
5. Automated or Assisted Response
In some implementations, AI can trigger initial response actions, such as isolating a compromised endpoint from the network, blocking suspicious traffic, escalating a high-priority alert, or notifying a human analyst for review. The level of automation varies significantly by organization. For high-impact decisions — like shutting down a server or locking a user account — human oversight is generally recommended.
How Is AI Used in Cybersecurity?
This is where AI cybersecurity has its most concrete real-world impact. The applications span nearly every domain of security operations.
AI for Threat Detection
AI threat detection involves analyzing large volumes of security telemetry — logs, network flows, endpoint data — to identify indicators of suspicious or malicious activity. Because AI can process this data at a scale and speed that human analysts cannot match alone, it helps organizations surface relevant threats faster than traditional monitoring approaches. AI models can correlate signals across different parts of the environment that might seem unrelated in isolation but together suggest a coordinated attack.
AI for Malware Detection
Traditional malware detection relies heavily on signatures: known patterns associated with known malicious files. AI malware detection complements this by analyzing behavior. Rather than looking for a specific file hash, a behavior-based AI system might flag a process that is encrypting large numbers of files unusually fast (a ransomware indicator), making unexpected network connections, or modifying system configurations in abnormal ways. This makes it possible to catch previously unseen malware variants that would bypass signature-only detection.
AI for Phishing Detection
Phishing remains one of the most common ways attackers gain initial access to systems. AI can analyze email signals — sender reputation, URL patterns, domain age, writing style, attachment characteristics, and language that attempts to create urgency — to identify potential phishing messages before users interact with them. Because AI-generated phishing emails are now being crafted by attackers to look highly legitimate, AI-powered detection that goes beyond simple keyword matching has become increasingly important for defenders.
AI for Network Security
AI-assisted network security involves monitoring traffic patterns across an organization’s environment to detect unusual behavior. This might include unexpected large data transfers, connections to suspicious external addresses, unusual protocol use, or lateral movement — where an attacker who has gained access to one system attempts to reach others. Network detection and response (NDR) platforms increasingly use machine learning models to perform this analysis continuously.
AI for Endpoint Security
Endpoints — laptops, desktops, servers, and mobile devices — are frequent targets of attack. AI-assisted endpoint detection and response (EDR) tools monitor the behavior of processes, files, and applications running on these devices. Rather than only scanning for known bad files, they watch for behavioral patterns that suggest malicious intent: unusual privilege escalation, process injection, suspicious script execution, and similar behaviors that indicate an attacker may be active on a device.
AI for Identity and Access Security
Unusual account behavior is often an early indicator of compromise. AI can analyze patterns such as impossible travel (a user logging in from two geographically distant locations within minutes), abnormal access to sensitive resources, unusual privilege use, or login activity at unexpected times. Identity-focused AI tools can flag these events for investigation or trigger step-up authentication requirements automatically, helping organizations detect both external attackers who have stolen credentials and insider threats.
AI for Security Operations Centers
Security operations centers (SOCs) are responsible for monitoring an organization’s security posture and responding to incidents. In practice, SOC teams are often overwhelmed by the volume of alerts generated by security tools — many of which are false positives. AI can help by correlating alerts across different data sources, reducing noise, prioritizing which incidents deserve immediate attention, and generating summaries that help analysts understand a situation quickly. AI-assisted investigation tools can also search across large datasets of security data in response to analyst queries, significantly accelerating the time it takes to understand what happened during an incident.
AI for Incident Response
When a security incident is identified, speed matters. AI can help incident response teams by organizing event timelines, surfacing related activity that might have been missed, identifying the scope of a compromise, and suggesting containment actions. While human judgment remains essential for major incident decisions, AI-assisted tools can reduce the manual effort required to piece together what occurred.
Benefits of AI in Cybersecurity
The growing adoption of AI-powered cybersecurity reflects genuine advantages that address real challenges organizations face.
Faster Threat Detection
Speed is one of the most significant advantages AI offers. Human analysts can examine only a limited number of alerts in a given period. AI systems can process millions of events continuously, identifying suspicious patterns within seconds rather than hours or days. Faster detection often translates to faster containment — reducing the time attackers have to cause harm.
Improved Scalability
Modern organizations generate enormous volumes of security data across cloud environments, remote endpoints, third-party systems, and internal infrastructure. Processing all of this manually would require prohibitively large security teams. AI allows organizations to analyze security data at a scale that would otherwise be impossible.
Automated Repetitive Tasks
A significant portion of security analyst time is spent on repetitive, lower-complexity tasks: triaging alerts, reviewing logs, categorizing threats, and writing incident tickets. Cybersecurity automation through AI can handle much of this work, freeing analysts to focus on tasks that require human judgment, context, and strategy.
24/7 Monitoring
Threats do not respect business hours. AI-powered systems can monitor security events continuously, without breaks, overtime costs, or fatigue. Human teams provide oversight and handle complex decisions, while AI handles continuous analysis.
Better Threat Prioritization
One of the most persistent challenges in security operations is alert fatigue — when analysts receive so many notifications that important threats get buried. AI can help score and prioritize alerts based on severity, context, and potential impact, helping teams focus on what actually requires urgent attention.
Faster Incident Response
Faster detection connects directly to faster response. When AI surfaces a high-priority threat and provides relevant context quickly, incident response teams can begin their work without spending hours gathering basic information about what occurred.
Support for Cybersecurity Professionals
Perhaps the most important benefit: AI should be understood as a force multiplier for skilled security professionals, not a replacement for them. It extends what a team can monitor, analyze, and respond to — but human expertise, judgment, and strategic thinking remain indispensable.
How Hackers Are Using AI
AI is not exclusively a defensive technology. Understanding how attackers use it is essential for building appropriate defenses.
AI-Generated Phishing
Generative AI has meaningfully raised the quality of phishing emails. In the past, many phishing messages were identifiable by awkward grammar, generic language, and obvious mistakes. Today, AI tools allow attackers to produce personalized, grammatically polished messages that convincingly impersonate a known colleague, a trusted organization, or a legitimate service. According to available industry reporting, AI-generated content has appeared in a growing proportion of observed phishing campaigns in 2025 and 2026. The personalization is particularly concerning: AI can tailor messages to a specific target using publicly available information, making each message harder to recognize as a scam.
Social Engineering
Beyond email, AI enables more convincing social engineering across channels — SMS, voice calls, and messaging platforms. Natural language generation tools make it easier for attackers to write persuasive messages at scale, targeting large numbers of individuals with highly plausible content.
Malware Development
AI tools can potentially assist attackers in developing or refining malicious code, though cybersecurity researchers note that human involvement remains central to sophisticated attack operations. The concern is less about AI autonomously creating malware and more about AI reducing the skill barrier for certain parts of the attack lifecycle.
Deepfakes and Impersonation
Deepfake technology — AI-generated synthetic audio, video, and images — has become one of the more alarming attack vectors. Attackers have used AI-cloned voices and realistic video to impersonate executives, instruct employees to transfer funds, and bypass identity verification processes. Reports of finance workers being deceived by AI-generated videoconference calls have drawn significant attention to this threat. The technology has become more accessible through commercial and underground services, making impersonation attacks more scalable than they once were.
Automated Reconnaissance
Before launching an attack, threat actors typically gather information about their targets. AI can assist in processing and analyzing publicly available information — from company websites, social media, job postings, and other sources — to identify potential targets, technology in use, and organizational structures faster than manual methods allow.
Key takeaway: AI can lower the cost and increase the speed of certain malicious activities, making layered cybersecurity defenses increasingly important. No single control is sufficient on its own.
AI Cybersecurity Risks and Limitations
A realistic assessment of AI in cybersecurity requires acknowledging its limitations as well as its strengths.
False Positives
AI systems can incorrectly flag legitimate activity as suspicious. A security analyst who receives too many false positives may begin to ignore alerts, creating real risk when a genuine threat is buried in the noise. Poorly calibrated AI models can make this problem worse rather than better.
False Negatives
AI can also miss real threats. Sophisticated attackers who understand how AI detection systems work can attempt to operate in ways that blend into normal-looking patterns — a technique sometimes called “living off the land.” No detection system catches everything.
Poor or Biased Training Data
AI models learn from historical data. If that data is incomplete, unrepresentative of real attack patterns, or reflects past conditions that no longer apply, the model’s decisions will be unreliable. Organizations deploying AI security tools need to understand the data that trained those systems.
Adversarial Attacks
This is an important and often underappreciated risk. Adversarial machine learning refers to techniques where attackers deliberately attempt to manipulate or deceive AI models. This might involve crafting inputs designed to avoid detection, feeding manipulated data into a model’s training process, or attempting to infer information about a model’s behavior in order to exploit it. NIST has published guidance addressing adversarial machine learning threats and mitigations, recognizing this as a significant security concern for organizations deploying AI systems.
Privacy Concerns
Cybersecurity systems that analyze behavior, communications, and access patterns necessarily process sensitive personal and organizational data. Organizations need to ensure their AI security tools handle this data in compliance with privacy requirements and data governance policies.
Lack of Explainability
Some AI models — particularly complex deep learning systems — produce decisions that are difficult for humans to understand or audit. When an AI system flags an event as suspicious, analysts may need to understand why in order to investigate effectively and make appropriate response decisions. Explainability matters both for operational effectiveness and for accountability.
Overreliance on Automation
Perhaps the most significant organizational risk is treating AI as infallible. AI security tools should augment human judgment, not replace it entirely. Organizations that over-automate responses or fail to maintain human oversight of high-impact decisions may find themselves taking incorrect actions during incidents or missing threats that AI systems fail to catch.
AI-Specific Security Threats
An important distinction: AI is not only a tool for cybersecurity. AI systems themselves need to be secured. As organizations deploy AI applications and agents, they create new attack surfaces that require specific attention.
OWASP, which produces widely used security guidance for application developers and organizations, has published both the Top 10 for LLM Applications (2025) and the Top 10 for Agentic Applications (2026) — two resources that address the security risks specific to AI-powered systems.
Prompt Injection
Prompt injection occurs when malicious instructions are embedded in inputs to an AI system in a way that manipulates the system’s behavior — causing it to ignore its intended instructions, produce harmful outputs, or take unintended actions. OWASP identifies prompt injection as one of the most critical risks for LLM-based applications. For example, an AI assistant that processes user documents or emails might encounter hidden instructions designed to change what the AI does with that content.
Sensitive Information Disclosure
AI applications — particularly those that use retrieval-augmented generation or have access to organizational data — can potentially expose sensitive information that should not be accessible to the user interacting with the system. Improperly configured AI applications may inadvertently surface confidential documents, internal data, or information from other users’ sessions.
Data and Model Poisoning
The integrity of an AI system depends on the integrity of its training data and, for retrieval-based systems, its reference data. Data poisoning attacks involve manipulating this data to cause the AI system to behave in harmful or inaccurate ways. CISA’s May 2025 AI data security guidance specifically calls out data poisoning as a key risk area and provides best practices for protecting data integrity across the AI lifecycle.
Supply-Chain Risks
Most organizations building AI applications rely on third-party models, datasets, libraries, plugins, and cloud-based AI services. Each of these dependencies represents a potential supply-chain risk. A compromised or malicious component in the AI supply chain can affect the security and reliability of the entire system. OWASP’s LLM security guidance identifies supply-chain vulnerabilities as a top concern, noting risks from third-party components and pre-trained models whose provenance has not been verified.
Excessive Agency
As AI agents become more capable of taking actions — sending emails, querying databases, executing code, calling APIs — the consequences of manipulation or error grow more serious. OWASP’s guidance on agentic applications highlights excessive agency as a critical risk: when AI agents have broader permissions or more autonomy than their tasks require, attackers who successfully manipulate them can cause significant harm. The principle of least privilege — giving AI agents only the access they actually need — applies as much to AI systems as it does to human users.
AI Cybersecurity Tools and Technologies
Rather than listing individual products, it is more useful to understand the categories of AI-powered security technology and what each is designed to do.
AI-Powered SIEM and SOC Platforms
Security information and event management (SIEM) platforms collect and correlate security events from across an organization’s environment. AI capabilities embedded in modern SIEM tools can analyze this data more intelligently — identifying patterns across large event volumes, reducing false positives, and surfacing high-priority incidents for human review. Some platforms incorporate generative AI to help analysts search security data using natural language queries.
Endpoint Detection and Response (EDR)
EDR tools monitor endpoint devices for suspicious activity. AI-assisted EDR goes beyond signature scanning by watching how processes behave — catching malicious behavior even from tools and techniques that have no known signatures. These tools can also provide investigation timelines and artifact analysis that help response teams understand what happened on a compromised device.
Network Detection and Response (NDR)
NDR tools apply machine learning to network traffic analysis, identifying anomalous behavior that may indicate intrusion, lateral movement, or data exfiltration. Because network traffic volumes are vast, AI is particularly valuable for processing this data continuously and at scale.
AI Threat Intelligence
Threat intelligence platforms use AI to process and analyze large volumes of indicators, reports, vulnerability data, and dark web content to help organizations understand current and emerging threats. AI can correlate signals from multiple sources to produce more actionable intelligence than manual analysis would allow.
Security Copilots and AI Assistants
An emerging category of AI security tools focuses on supporting analysts directly. These tools can summarize complex security events in plain language, answer natural-language queries about security data, draft incident reports, suggest investigation steps, and explain technical findings in accessible terms. Several major cybersecurity vendors have introduced AI assistant capabilities specifically for security operations.
AI Cybersecurity vs Traditional Cybersecurity
| Area | Traditional Cybersecurity | AI-Powered Cybersecurity |
|---|---|---|
| Detection | Rules / signatures | Behavior + patterns |
| Data volume | More manual analysis | Large-scale analysis |
| Automation | Moderate | Higher potential |
| Unknown threats | Can be more challenging | Can identify anomalies |
| Human involvement | High | Still essential |
| Explainability | Often clearer | Can be more complex |
The right conclusion from this comparison is not that AI replaces traditional cybersecurity — it is that AI is another layer of the security stack. Organizations that rely exclusively on AI while abandoning security fundamentals would be making a mistake. The most effective security programs combine solid foundational controls with AI-powered capabilities that extend what teams can detect and respond to.
How Businesses Can Use AI Safely for Cybersecurity
Adopting AI cybersecurity tools requires more than purchasing software. Organizations that approach it thoughtfully will get better results and manage the associated risks more effectively.
Start With a Clear Security Problem
Organizations should resist the temptation to adopt AI simply because it is trending. The most effective implementations start with a clearly defined security challenge — reducing alert fatigue, improving phishing detection, accelerating incident investigation — rather than deploying AI and hoping it finds problems.
Protect Sensitive Data
AI security tools necessarily access sensitive data about organizational behavior, communications, and systems. Organizations should implement data governance policies, apply access controls to security data, practice data minimization, and ensure AI vendors handle data in compliance with applicable privacy requirements.
Keep Human Oversight
For high-impact security decisions — isolating systems, blocking accounts, escalating to leadership, communicating externally about incidents — human oversight should remain in place. Fully automated responses are appropriate for low-risk, well-understood situations, but humans should retain authority over decisions with significant operational consequences.
Test AI Systems
Before deploying AI security tools in production, organizations should evaluate their accuracy, false-positive rates, false-negative rates, and failure modes. AI systems should also be tested for adversarial robustness — how they respond to inputs deliberately designed to manipulate them.
Monitor Continuously
AI security systems themselves need monitoring. Models can drift over time as the environment changes. Organizations should track performance metrics and retrain or reconfigure models when they begin to underperform.
Create an Incident Response Plan
Even with AI-assisted detection and response, organizations need documented incident response plans that cover scenarios where automated systems make incorrect decisions, produce unexpected actions, or are themselves compromised.
Follow Established Frameworks
NIST’s AI Risk Management Framework and Cybersecurity Framework, CISA’s AI data security guidance, and OWASP’s LLM and agentic security resources provide practical, authoritative starting points for organizations building secure AI-enabled security programs.
The Future of AI Cybersecurity
The trajectory of AI in cybersecurity points toward both greater capability and greater complexity on both sides of the security equation.
Security operations centers are likely to become increasingly AI-assisted, with analysts working alongside AI tools that handle routine analysis, surface relevant context, and reduce the cognitive load of monitoring large environments. AI agents — systems that can take sequences of actions autonomously — will probably play a larger role in security operations, handling selected investigation and response tasks under human supervision.
On the attacker side, AI-assisted attacks are expected to continue growing in sophistication and volume. Phishing operations are already more scalable and more convincing because of generative AI, and this trend is likely to intensify. Adversarial techniques targeting AI detection systems themselves will also become more sophisticated.
This creates a dynamic that NIST and CISA have both described in recent guidance: organizations will need to protect not just their infrastructure, but also the AI systems embedded within it. The governance of AI security — questions about accountability, oversight, and the appropriate limits of automation — will become increasingly important.
The future of cybersecurity may not simply be AI versus hackers. It may increasingly involve AI-assisted defenders facing increasingly AI-assisted attackers. The competitive advantage will belong to organizations that use AI responsibly, govern it carefully, and ensure that skilled human professionals remain at the center of critical security decisions.
Can AI Replace Cybersecurity Professionals?
The direct answer is: AI is unlikely to completely replace cybersecurity professionals.
What AI is genuinely good at is processing data at scale, recognizing patterns across millions of events, performing repetitive analytical tasks without fatigue, and surfacing relevant information faster than human review allows. These capabilities meaningfully improve what security teams can accomplish.
But cybersecurity involves far more than data processing. Effective security professionals bring contextual understanding that AI currently lacks — they know how a specific organization operates, understand its risk tolerance, navigate relationships with leadership and business units, and make judgment calls that require ethical reasoning and organizational knowledge. Complex investigations often involve piecing together fragmented signals with incomplete information, using creative thinking that remains distinctly human. Incident leadership, regulatory communication, risk decisions, and security strategy all require human judgment that cannot be automated away.
The more likely direction is a continued shift toward AI-augmented cybersecurity professionals — security teams where AI handles high-volume routine analysis while human experts focus on strategy, investigation, decision-making, and leadership. Organizations that invest in helping their security professionals work effectively alongside AI tools are better positioned than those trying to choose between the two.
Even More people say that the Ai Replace job but you can break that myth For Get actual data Read this : Ai Replace Jobs in 2030 ?
11. FAQ Section
What is AI cybersecurity?
AI cybersecurity refers to the use of artificial intelligence and machine-learning techniques to identify, analyze, prevent, prioritize, and respond to cybersecurity threats. Rather than relying solely on known-threat signatures or manually written rules, AI-powered security systems learn from data to detect both known threats and unusual patterns that may signal new attacks.
How is AI used in cybersecurity?
AI is used across many areas of cybersecurity: detecting threats in network traffic and endpoint behavior, identifying phishing emails, analyzing malware behavior, correlating security alerts in operations centers, supporting faster incident response, and assisting analysts through AI-powered tools and security copilots.
Can AI detect cyber attacks?
Yes, AI can detect a wide range of cyber attack indicators — unusual login patterns, suspicious network behavior, malware-like process activity, and phishing characteristics, among others. However, AI is not perfect. It can generate false positives (flagging legitimate activity) and false negatives (missing real threats), which is why human oversight and a layered security approach remain important.
What are the benefits of AI in cybersecurity?
The main benefits include faster threat detection, improved scalability across large environments, automation of repetitive tasks, continuous 24/7 monitoring, better threat prioritization, faster incident response, and support for security professionals who would otherwise be overwhelmed by alert volume and data complexity.
What are the risks of AI cybersecurity?
Risks include false positives and false negatives, dependence on high-quality training data, vulnerability to adversarial attacks that manipulate AI models, privacy concerns from processing sensitive data, limited explainability in some AI systems, and the organizational risk of overrelying on automation while reducing human oversight.
Can hackers use AI?
Yes. Attackers are using AI to generate more convincing and personalized phishing emails, create deepfake audio and video for impersonation, automate parts of their operations, and potentially assist in malware development. AI has lowered certain barriers for attackers, making it more important for defenders to adopt layered security controls that do not rely on any single detection method.
Can AI replace cybersecurity professionals?
AI is unlikely to replace cybersecurity professionals. It can automate high-volume, repetitive analytical tasks and help analysts work more effectively, but it cannot replicate the contextual judgment, strategic thinking, ethical reasoning, and organizational knowledge that skilled security professionals provide. The more realistic outcome is AI-augmented security teams where both human expertise and AI capabilities complement each other.
What is the future of AI in cybersecurity?
AI will likely play a growing role in security operations, with AI agents taking on more investigative tasks under human supervision and AI assistants helping analysts navigate complex environments more efficiently. At the same time, AI-assisted attacks will continue to grow in sophistication. Organizations will need to protect both their infrastructure and their AI systems — and governance of AI in security will become increasingly important.
12. External Links
| Source | Suggested Anchor Text | URL | Purpose |
|---|---|---|---|
| NIST | Draft NIST Cyber AI Profile | https://www.nist.gov/news-events/news/2025/12/draft-nist-guidelines-rethink-cybersecurity-ai-era | Support AI/cybersecurity framework explanations |
| NIST | NIST AI Risk Management Framework | https://www.nist.gov/system/files/documents/2023/01/26/AI%20RMF%201.0.pdf | Support AI risk and governance section |
| CISA | CISA Artificial Intelligence | https://www.cisa.gov/ai | Support defensive best practices and organizational guidance |
| CISA | CISA AI Data Security Guidance (May 2025) | https://media.defense.gov/2025/May/22/2003720601/-1/-1/0/CSI_AI_DATA_SECURITY.PDF | Support data poisoning and supply-chain risk sections |
| OWASP | OWASP Top 10 for LLM Applications | https://owasp.org/www-project-top-10-for-large-language-model-applications/ | Support prompt injection, sensitive data, and supply-chain risk sections |
| OWASP | OWASP Top 10 for Agentic Applications 2026 | https://genai.owasp.org/resource/owasp-top-10-for-agentic-applications-for-2026/ | Support agentic AI and excessive agency risk section |